

September 7, 2026 By Bill Toulas
A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal more than 5,000 Microsoft 365 credentials.
Researchers at cybersecurity company CloudSEK gained administrator access to the control panel and found that the service managed 42 VPS nodes, all configured to target Microsoft 365 as part of the observed operation.
According to the researchers, the campaign uses an Evilginx2-based adversary-in-the-middle framework to intercept passwords and authenticated session cookies, allowing attackers to hijack accounts after victims complete the multi-factor authentication (MFA) process.
BigBear uses a configuration called “offy” that sets up a man-in-the-middle (AiTM) proxy between the victim and Microsoft’s legitimate authentication infrastructure.
This allows the attacker to capture credentials, including MFA, and session cookies and replay them through an API to hijack the victim’s authentication session.
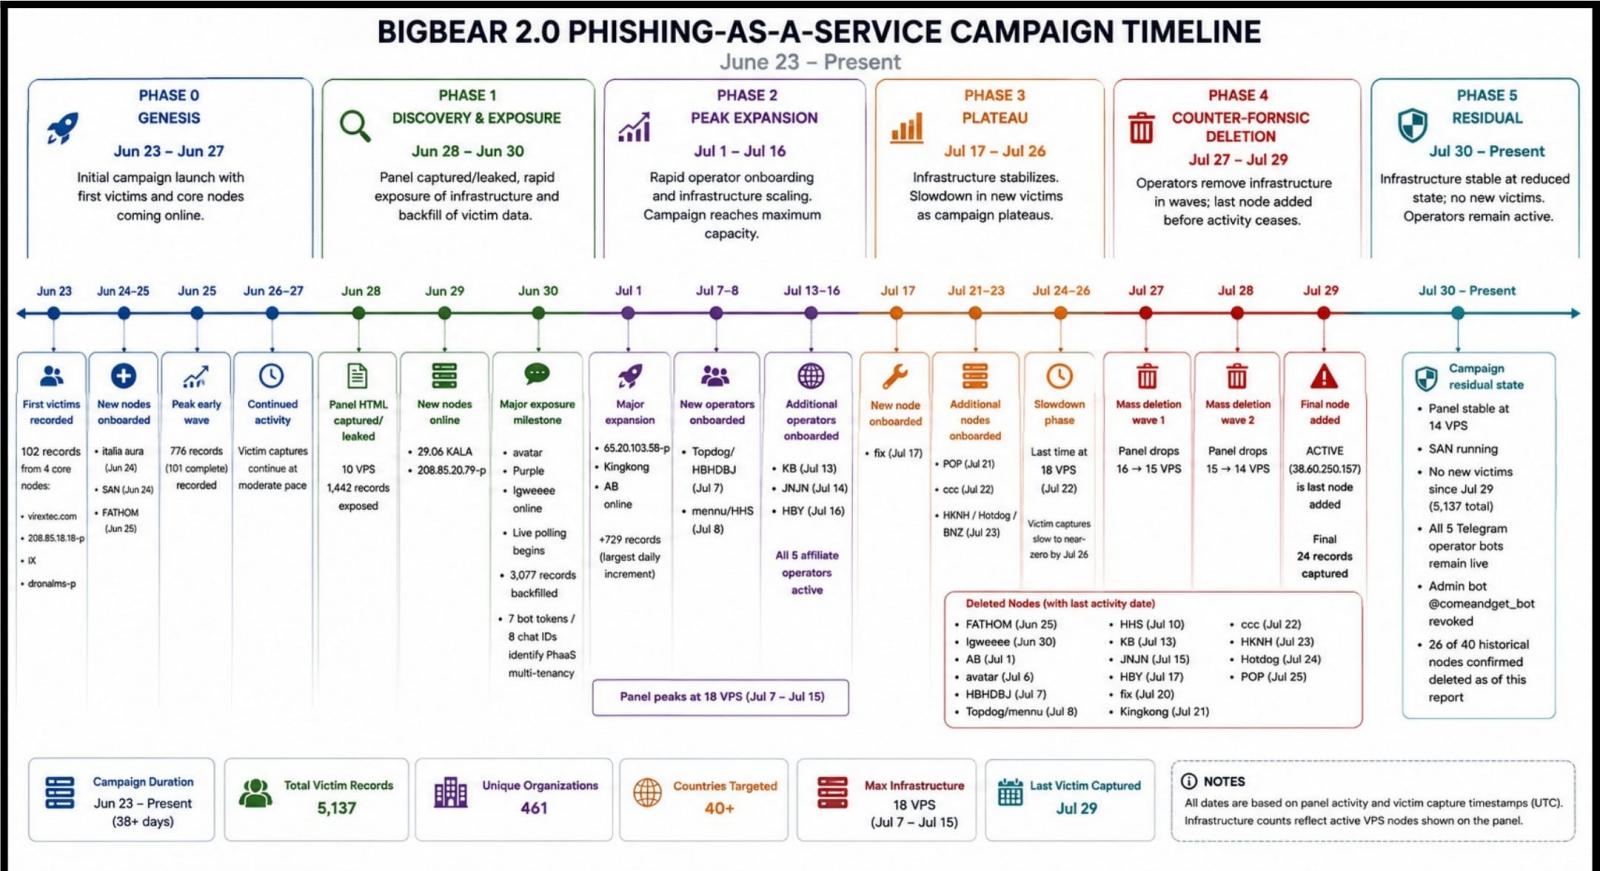
Source: CloudSEK
Microsoft 365 is Microsoft's cloud productivity and identity ecosystem, incorporating services such as Exchange Online, Teams, SharePoint, OneDrive, and Entra ID authentication.