Electronic signature platforms have become a routine part of business operations, making them an attractive lure for threat actors. While DocuSign remains the most commonly spoofed brand, attackers are increasingly abusing alternative document-signing services and trusted email infrastructure to make their campaigns appear legitimate.
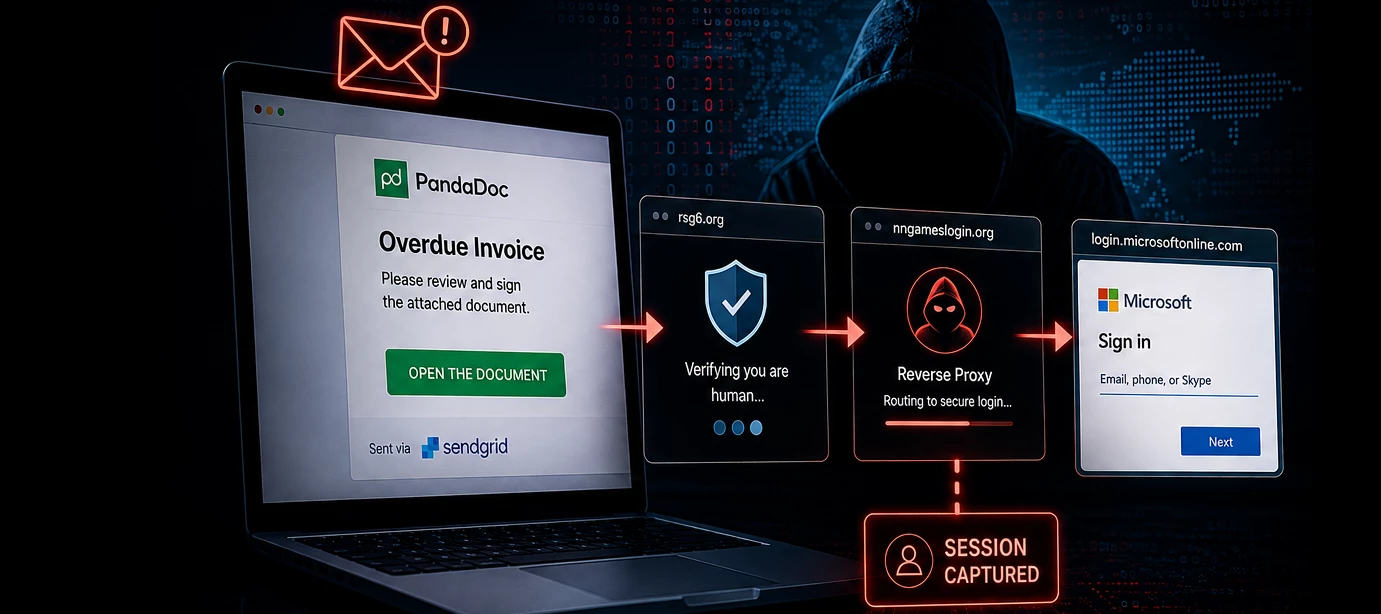
A recent campaign observed by our team illustrates this evolution. The attack impersonated PandaDoc and claimed that overdue invoices required review and signature, leveraging a workflow that many finance, procurement, and accounts payable employees encounter regularly
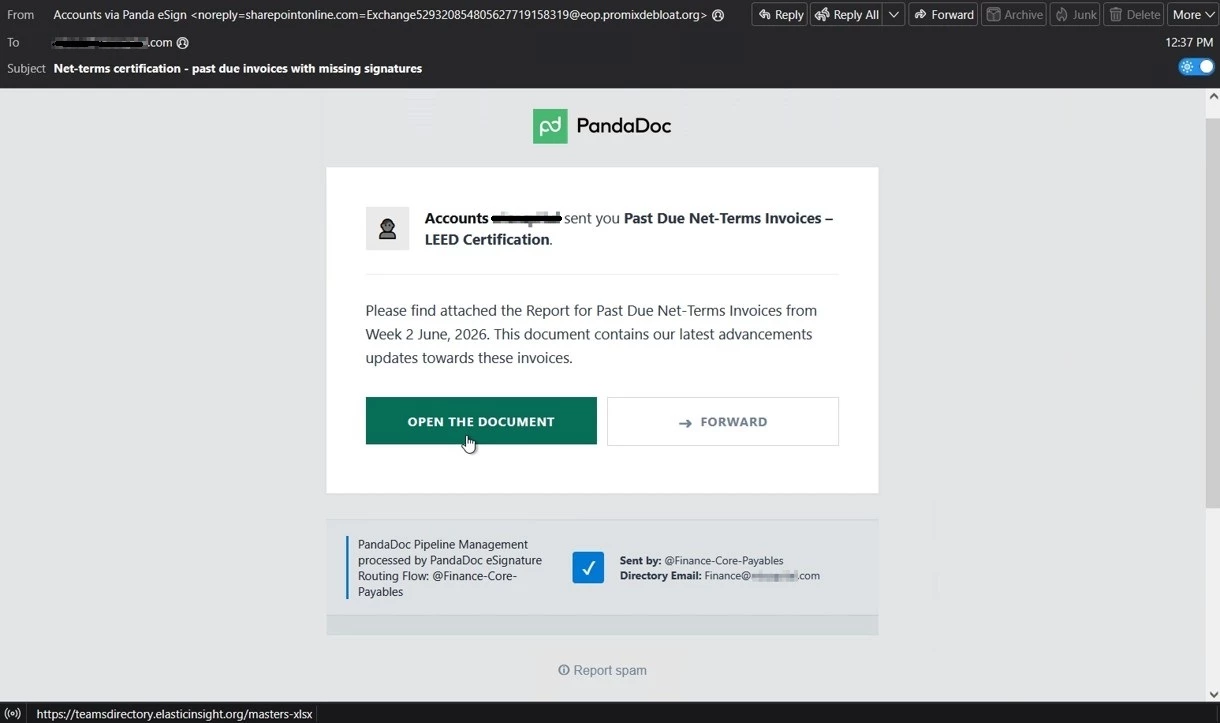
The email was delivered through a compromised SendGrid account and legitimate SendGrid infrastructure. Rather than building trust from scratch, the attackers inherited credibility from an established business communications platform, increasing the likelihood that the message would reach inboxes and be viewed as authentic.
Clicking "OPEN THE DOCUMENT" did not immediately direct users to a login page. Instead, recipients were routed through an intermediary site hosted at rsg6[.]org.
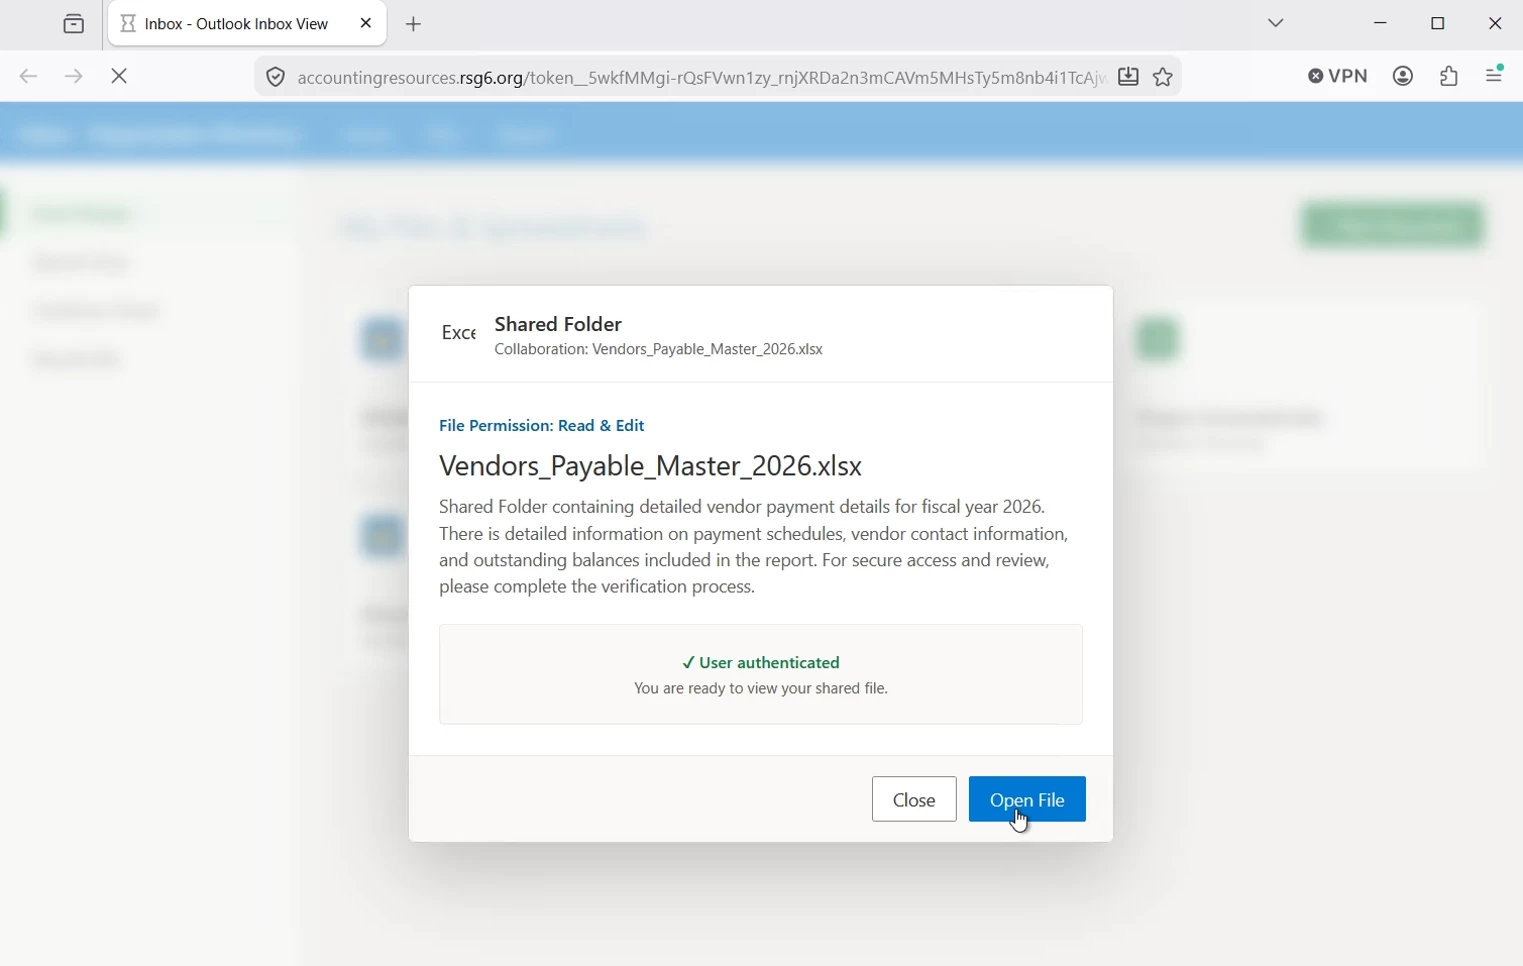
This intermediary page appears designed to distinguish real users from automated security scanners and link-analysis tools. By filtering traffic before victims reach the final stage, attackers can reduce early detection and prolong the lifespan of their infrastructure.
The growing use of human-verification stages demonstrates how phishing operators are increasingly focused on defeating automated defenses, not just deceiving users.
Users who progressed beyond this stage were directed to infrastructure hosted at nngameslogin[.]org. Rather than functioning as a traditional credential harvesting page, the site operated as a reverse proxy positioned between the victim and a legitimate authentication service.
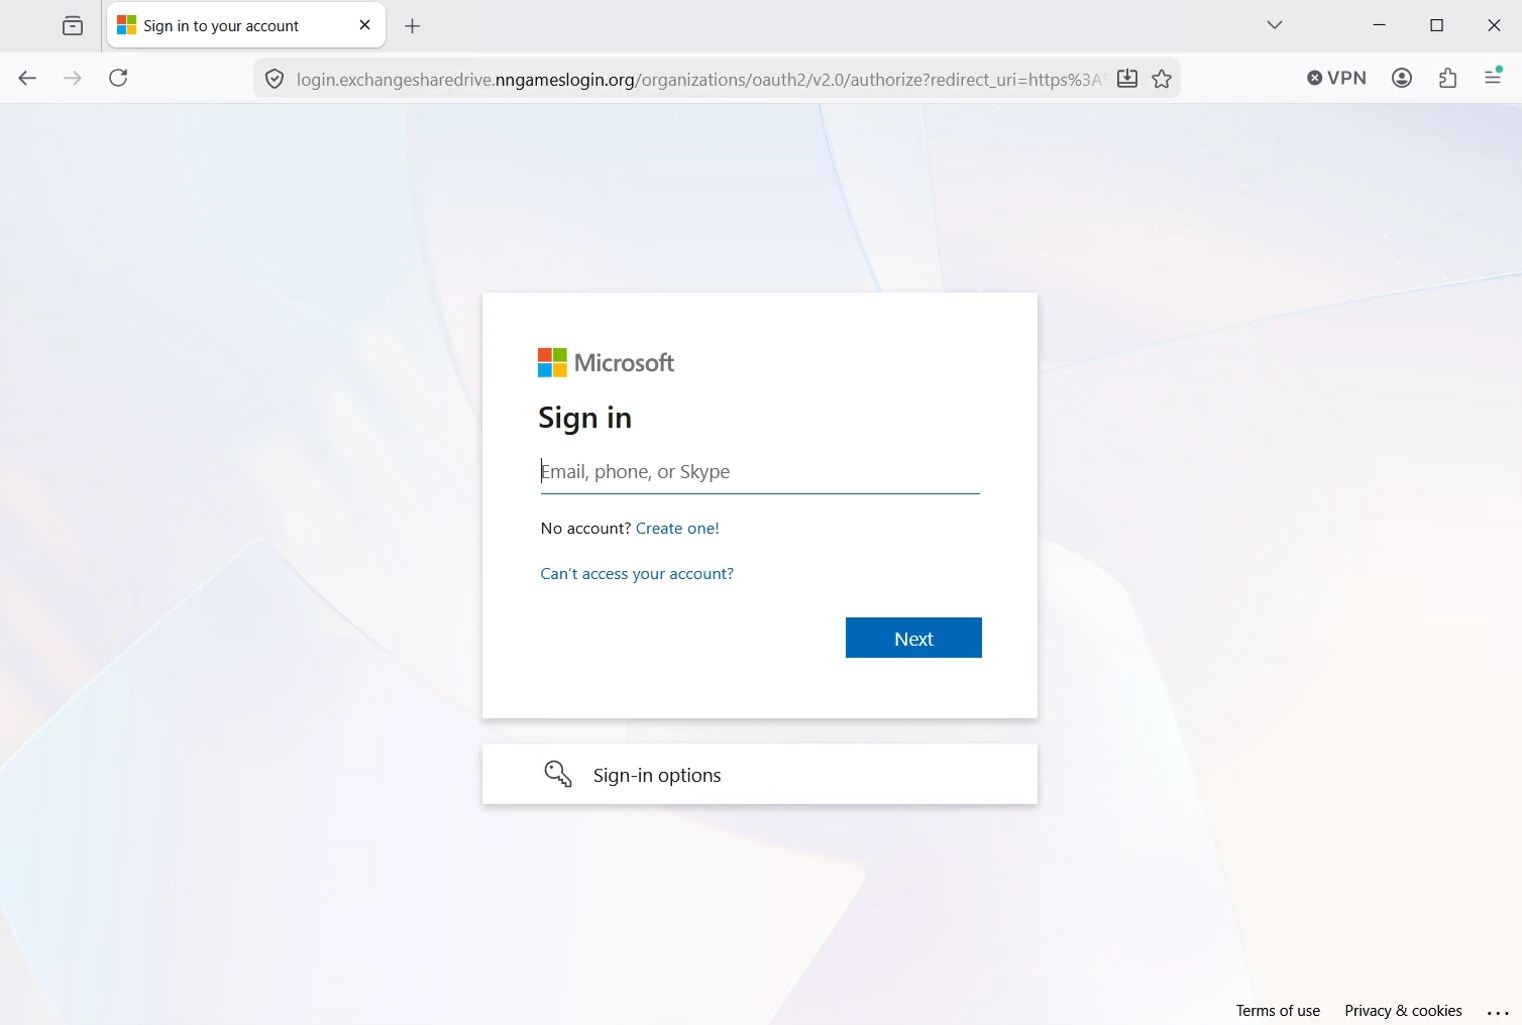
Reverse-proxy phishing frameworks have become popular because they can capture authenticated sessions in addition to credentials. In environments protected by multi-factor authentication, a stolen session may be far more valuable than a password alone.
Modern phishing campaigns are increasingly focused on stealing authenticated access rather than simply collecting credentials.
The most significant takeaway is that phishing operators are increasingly engineering their infrastructure around security products rather than victims. In this campaign, the compromised SendGrid account addressed email reputation controls, the intermediary verification page filtered automated analysis, and the reverse-proxy framework targeted modern authentication protections.
The result was an attack chain designed to defeat multiple layers of defense before relying on social engineering alone. Rather than deploying a simple phishing page and hoping for user interaction, the operators assembled specialized components for delivery, security evasion, and session interception. This modular approach reflects how phishing operations continue to mature, with attackers investing as much effort in bypassing organizational security controls as they do in convincing users to click.
For defenders, the lesson extends beyond identifying suspicious emails or malicious domains. Modern phishing campaigns are increasingly composed of legitimate services, compromised business infrastructure, and adversary-in-the-middle frameworks that can undermine traditional credential-based security controls. As these attacks evolve, successful detection will depend on understanding the full attack chain rather than any single indicator in isolation.