Webroot Endpoint Protection
What is being released?
Mac Endpoint Protection Agent for Business Version 9.8.5.53 was released including the Consumer version of the agent.
Key Highlights
For Business -
-
Device Isolation Improvement
Resolved an issue associated with device isolation actions performed through the Pillr Console, improving the reliability of device isolation and restoration.
-
Enhanced Policy and Network Logging
Introduced enhanced logging for policy checks and network connectivity activity, providing greater visibility into policy propagation and system behavior. This helps administrators more effectively audit operations, troubleshoot issues, and ensure reliable policy enforcement.
For Business & Consumer-
-
Internal Scan Reporting Improvements
Improved internal scan reporting workflows by moving scan reporting responsibilities to dedicated platform components. Existing scan visibility, reporting, and threat telemetry behavior have been preserved.(This is not customer facing change)
-
Offline License Validation Improvements
Resolved an issue where WSA for Mac could incorrectly display an "Invalid Keycode" message while offline despite having a valid license. The application now correctly retains and validates licensing information during extended offline periods.
-
Security Status Reporting
Resolved an issue where the application status could remain in a warning state after successful malware remediation. The application now correctly updates to reflect the current protection status.
For Consumer-
-
Seamless Upgrade from WSA to Webroot Total Protection (WTP)
Webroot SecureAnywhere (WSA) can now seamlessly upgrade to the rebranded Webroot Total Protection (WTP) application, helping ensure uninterrupted protection and a smooth transition to the latest product experience.
Webroot Secure VPN 2.2.0 on iOS
What is being released?
We are excited to announce that the enhanced Webroot Secure VPN experience for iOS is now officially live on the Apple App Store.
Salient Features
-
Create Your Account In-App
New users can now create a Webroot account directly within the app and get connected in just a few simple steps.
-
Subscribe In-App
Customers can now purchase a Webroot Secure VPN subscription through Apple's In-App Purchase platform, creating a seamless onboarding and setup experience.
-
7-Day Free Trial
Users can experience Webroot Secure VPN free for 7 days before their subscription begins.
-
Performance Improvements
General bug fixes, stability updates, and performance enhancements deliver a smoother and more reliable VPN experience.
Value Delivered
This release simplifies the customer journey by:
-
Reducing onboarding friction for new users.
-
Enabling seamless subscription and payment directly within the app.
-
Improving conversion opportunities through a 7-day free trial.
-
Enhancing overall app performance and reliability.
OT Server Backup Windows Agent 9.50
What is being released?
OT Server Backup Windows Agent 9.50
New Features and Enhancements:
-
Support for SQL Server 2025
SQL Server 2025 and SQL Server Express 2025 are now supported with the Image Plug-in and SQL Server Plug-in.
-
Security enhancements
Security enhancements have been added in this Windows Agent version.
Webroot Security Awareness Training
New Feature Release:
This release introduces AI-powered email template creation in WSAT, giving admins/MSPs the ability to create customized phishing simulation templates on demand using a simple prompt.
Previously, admins/MSPs primarily relied on templates released through the global library and manual creation. With GenAI, they can now create content tailored to their specific needs, review and refine it, and save approved templates to their content library.
Key customer value:
-
Create content on demand instead of waiting for centrally released templates.
-
Expand campaign options by combining Global Library content with AI-generated Site Library templates.
-
Reduce manual effort and accelerate campaign creation.
-
Keep admins in control with a human-in-the-loop review and approval experience.
What is being released?
-
AI-powered email template creation :- Admins can enter a prompt and generate customized phishing simulation email templates.
-
Admin review & approval :- AI-generated content can be reviewed and edited before being approved for use.
-
Site Library integration :- Approved AI-generated templates are saved to the content library and can be reused in campaigns.
-
Global + Site Library experience :- Admins can choose from centrally curated templates or create and use their own AI-generated template.
-
AI usage controls :- Monthly AI credits provide governed and predictable usage.
OpenText Cloudally Backup CE 26.3.1
We are pleased to announce our new release for OpenText Cloudally Backup!
Release Highlights
-
Distributors: Enhanced Partner Portal Dashboard
We have redesigned the Distributor Dashboard in Partner Portal to make partner management faster, more intuitive, and more efficient.
We have introduced a modernized dashboard with new capabilities.
Key Enhancements:
-
Modernized dashboard with a refreshed user interface for a cleaner and more intuitive experience.
-
New Homepage layout with separate Partners and Direct Customers tabs, making it easier to navigate between the two views.
-
New Overview section at the top of the Partners tab, providing an at-a-glance summary of backup and billing status across all partners, enabling distributors to identify issues sooner.
-
Enhanced search and filtering capabilities, enabling distributors to quickly locate partners and identify operational or billing issues.
-
REST API Enhancements for Partners User Management
This release expands Cloudally API capabilities by introducing new user management endpoints for partners.
Key Enhancements:
-
New Distributor User Management API
Create users for the distributor account or any of the distributor's reseller accounts.
-
New Reseller User Management API
Create users for the reseller account.
-
Granular Access Configuration
When creating a user, partners can define user role, permissions, enabled backup services and accessible customer accounts.
-
User Deletion APIs
Added corresponding user deletion endpoints for both distributors and resellers, enabling complete user lifecycle management through REST APIs.
Microsoft Entra ID Backup Beta
We’re excited to announce that CloudAlly Entra ID Backup is now available as a limited beta.
The initial beta release focuses on backing up and recovering Entra ID users, groups, and roles, helping organizations protect critical identity data and recover from accidental deletion, misconfiguration, or cyber incidents.
There are currently ~50 partners participating in the beta and we are looking for their feedback to help improve our product.
If your partner or customer is interested in participating in the beta program, please send their details to @zix-CloudAlly Product.
As part of the beta program, the service is provided at no additional cost within the CloudAlly Microsoft 365 bundle.
OpenText Core Business Communication Archive (BCA)
What is being released?
Archive Customer Relationship Access and Control - OpenText Core Business Communication Archive (BCA) has introduced a new, faster way to share archived information with associated outside parties. You can now share archived communications with another BCA customer's archive through a controlled, admin-managed connection. The organization receiving the messages initiates a request, and the sending organization's admin chooses which users' incoming messages to share. Both parties can cancel the connection at any time.
What it means for customers
This update was made for those organizations responsible for overseeing the communications of another entity for regulatory purposes.
Broker-dealers who perform compliance oversight for Registered Investment Advisors (RIAs) can now receive copies of incoming archived messages directly into their own archive for review, without accessing or disrupting the RIA's environment. The same applies to Healthcare Management Services Organizations overseeing Healthcare providers, or parent companies that need visibility into subsidiary communications.
Previously, this type of oversight required manual processes or workarounds that introduced compliance risk and operational friction. Now, the connection is direct, auditable, and fully under admin control on both sides.
OpenText Secure Cloud
What is being released?
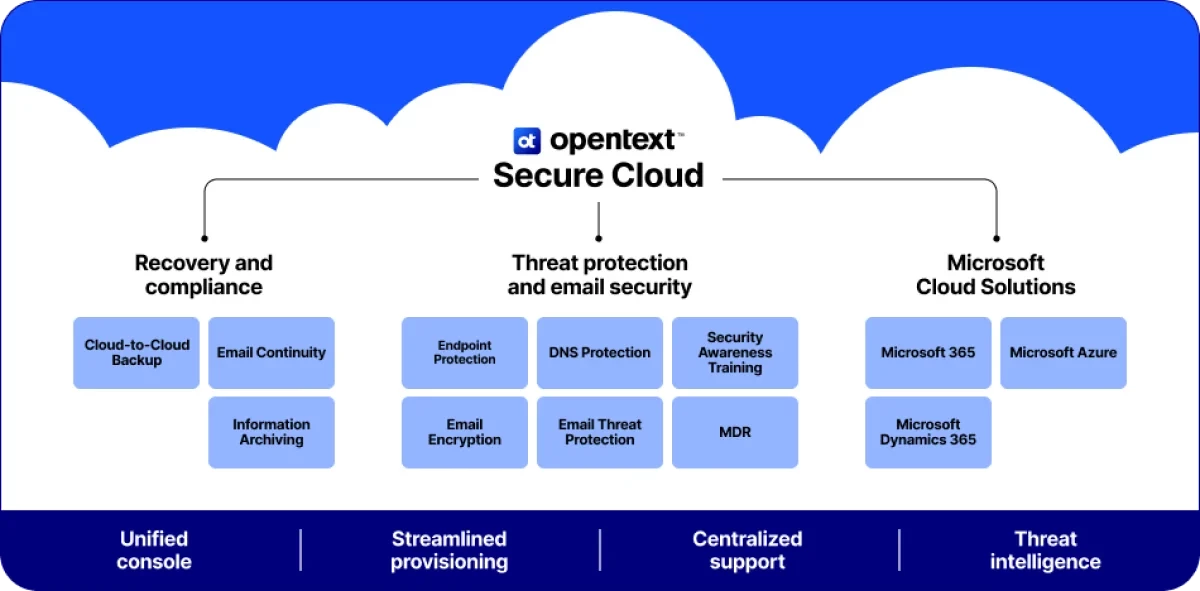
We are pleased to announce the availability of Hatz.AI as a NEW product that can now be ordered via Secure Cloud.
What is Hatz.AI?
Hatz.AI is a secure AI platform designed for managed service providers (MSPs) to build, deploy, and manage AI-powered workflows and agents. With no-code automation, multi-LLM capabilities, and enterprise-grade security, Hatz helps organizations streamline operations, improve productivity, and scale AI adoption with confidence.
Customers Impacted:
-
All Existing Secure Cloud Partners in the below regions
Regions Impacted
-
North America
-
EMEA
OpenText Core Endpoint Backup
We are excited to complete the roll out of OpenText Core Endpoint Backup v.11.7.
It includes new features such as:
-
Backup for individual files via file path - enables administrators and users to protect single files using their exact file paths, including browser bookmarks in Chrome and Edge on Windows and macOS.
-
Dashboard homepage update - our updated dashboard homepage helps administrators spot potential issues faster by putting backup status into a single view, including backup health, at-risk devices, activation status and more.
-
User ID added to Download User List - we've made it easier to identify users and quickly resolve admin tasks by adding a User ID column in the Download User list.
-
Dashboard Restore Error Messages - with new dashboard restore error notifications, administrators can quickly identify and act on restore failures right from the dashboard
-
Modernized Dashboard Service APIs - the WCF/SOAP Dashboard Service API has reached End of Life and is no longer supported. OpenText Core Endpoint Backup now exclusively supports REST APIs.
Here is the link to the detailed release notes: https://support.carbonite.com/endpoint/articles/Carbonite-Endpoint-Protection-Release-Notes
OpenText Detection & Response Portal 26.3.1 for OpenText EDR & MDR
What is being released?
I am pleased to announce the release of the Detection & Response Portal 26.3.1 for OpenText EDR & MDR.
This release helps partners understand which alerts are handled by the SOC and which alerts require partner action. It also adds structured SOC escalation settings, improves in-product guidance, and addresses customer-reported issues affecting workflows, reports, integrations, provisioning, permissions, and portal security.
New Features and Enhancements
Alert Ownership and SOC Visibility
-
Adds SOC handling information to new alerts: New alerts identify whether they are within the scope of SOC handling or remain the partner’s responsibility. This helps partners understand who is expected to respond without separately checking the customer’s product level and alert category.
-
Adds filtering by SOC handling responsibility: Partners can filter new alerts based on SOC handling status, making it easier to focus on alerts that require partner action.
-
Adds customer entitlement information to new alerts: New alerts can show whether the affected customer has EDR, Core MDR, or MDR Complete, providing additional context for partners managing customers with different service levels.
Important note about existing alerts
Customer entitlement and SOC handling information will be added to alerts created after Portal 26.3.1 is deployed. Existing alert records will not be updated with this information because reliably rebuilding the entitlement and handling status for historical alerts would introduce significant data accuracy and processing concerns.
For alerts created before the release:
-
The alerts will remain available in the All Alerts view.
-
Alerts without SOC handling information will not appear when filtering by SOC: Managed or SOC: Not Managed.
-
The SOC Managed column will display Unknown when SOC handling information is unavailable.
Support guidance: Do not use the Not Managed label by itself to determine responsibility for an alert created before Portal 26.3.1. If responsibility needs to be confirmed for an older alert, check the alert date, the customer’s entitlement, and the applicable SOC coverage separately.
SOC Escalation Configuration
-
Adds structured escalation contact settings: Partner administrators can maintain the contacts the SOC should use during an incident, including contact information, availability, and escalation order.
-
Supports business-hours and off-hours contacts: Partners can identify which contacts are available during each period and the order in which the SOC should attempt to reach them.
-
Adds disruptive-action consent: Partners can record whether the SOC is authorized to take response actions that may affect endpoint or business operations. This gives the SOC clearer guidance during an active incident.
-
Adds an escalation-setup reminder: Authorized users receive a non-blocking reminder when escalation configuration has not been marked complete, with a direct path to the appropriate settings.
-
Highlights escalation contact setup during onboarding: The onboarding guide now calls attention to the new escalation contact settings so partners know to configure their contacts, availability, escalation order, office hours, and disruptive-action consent.
Portal Guidance and Access
-
Adds the ability to replay portal guidance: Users can select Replay Tour from the user menu to revisit applicable in-product guidance after dismissing it.
-
Strengthens read-only access: Reader users can view the information available to them but cannot create, update, or delete portal records.
Fixes
Workflows and Notifications
-
Improves international workflow notifications: Fixes SMS and phone-call workflow notifications for some international numbers, including affected UK numbers.
-
Improves SMS delivery across alert triggers: Fixes an issue where SMS workflow tasks could work for some alert types but fail for others.
-
Preserves existing SOC escalation behavior: Existing workflows that use the previous SOC escalation process continue to route as expected, while newly created escalation actions follow the current SOC handling model.
Reports
-
Restores vulnerability report exports: Fixes a customer-reported issue that prevented some users from exporting vulnerability findings to CSV.
-
Restores Monthly Metrics report delivery: Fixes an issue where Monthly Metrics report requests appeared to succeed, but the report was not generated or delivered by email.
Integrations
-
Corrects Microsoft licensing warnings: The Microsoft integration now recognizes supported Microsoft Entra ID P1 entitlements included with bundled Microsoft licenses, preventing incorrect warnings that the license is missing.
-
Improves Autotask customer mapping: Fixes an issue where the Autotask customer-mapping section could fail to load or show incorrect configuration information.
-
Improves Webroot integration recovery: Fixes an issue where some Webroot integrations could remain in an error state after the user successfully completed single sign-on.
Portal Security and Data Reliability
-
Corrects portal logout behavior: Logging out now ends the active Portal session so users must authenticate again before regaining access. This is particularly important when the Portal is accessed from shared devices or administrator workstations.
-
Prevents duplicate provisioning records: Adds safeguards to prevent duplicate customer and subscription records from being created during provisioning.
-
Corrects SOC escalation for inactive MDR subscriptions: Alerts are no longer sent to the SOC when the customer does not have an active MDR subscription.
OpenText Management Console (GSM)
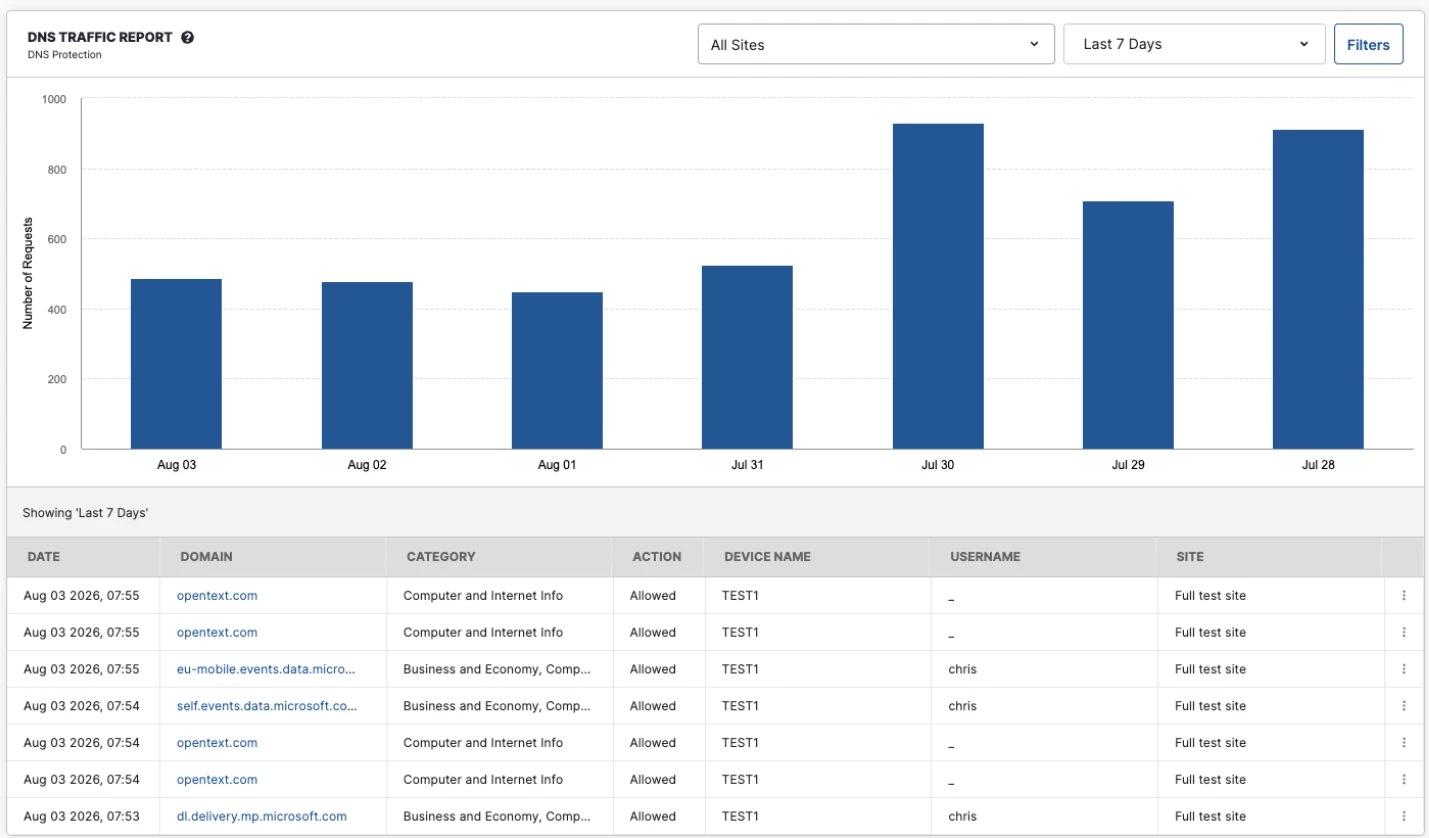
We are excited to announce several new and updated DNS Reports, giving partners deeper visibility into DNS traffic and activity.
What is being released?
This release introduces several new features, including new DNS Reports as well as updates to existing ones:
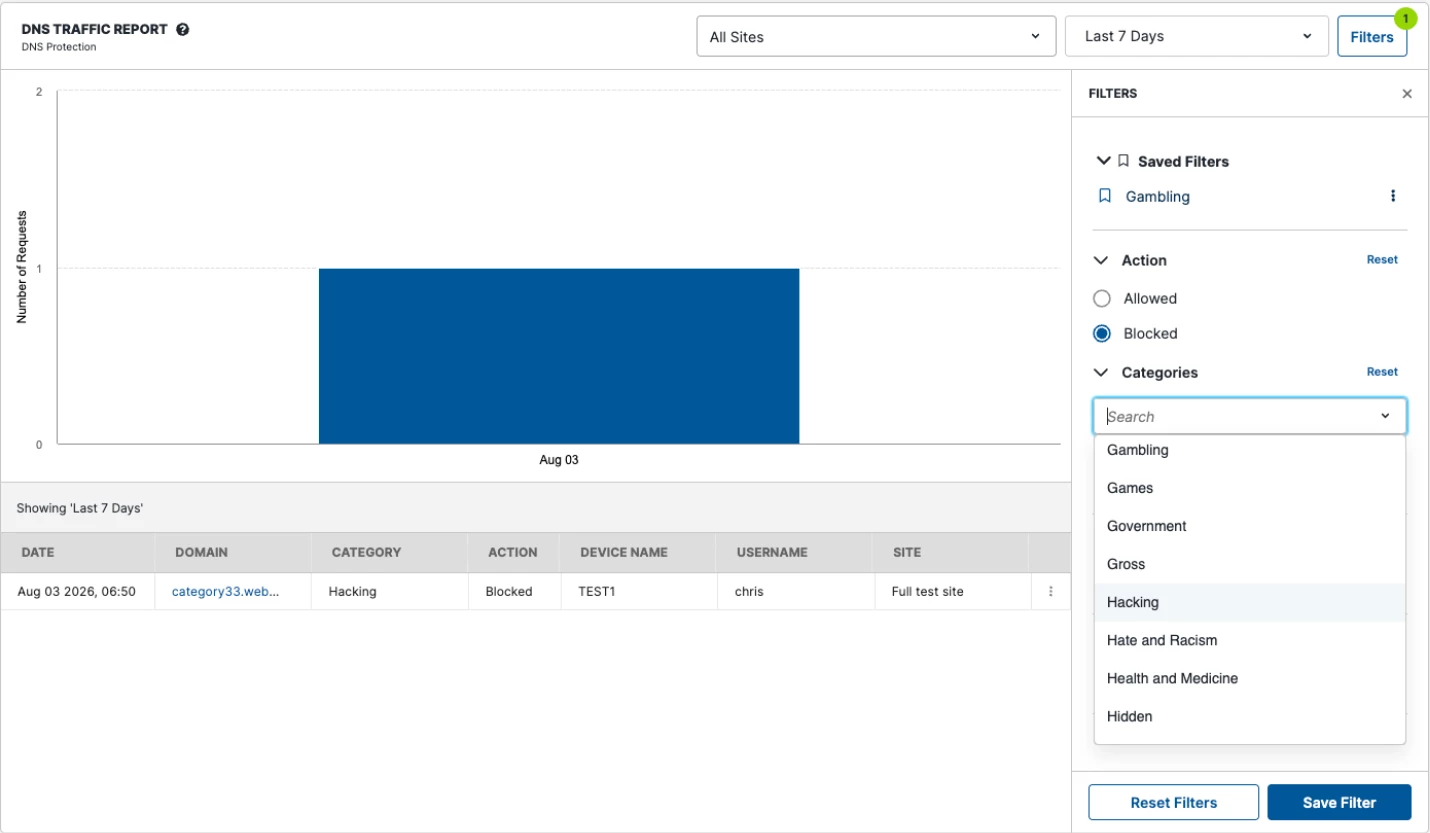
DNS Traffic Report replaces the Active Host Report, with several new features:
-
Filter based on Action and Category
-
Search for a specific Domain
-
Refine results to a specific User or Device
-
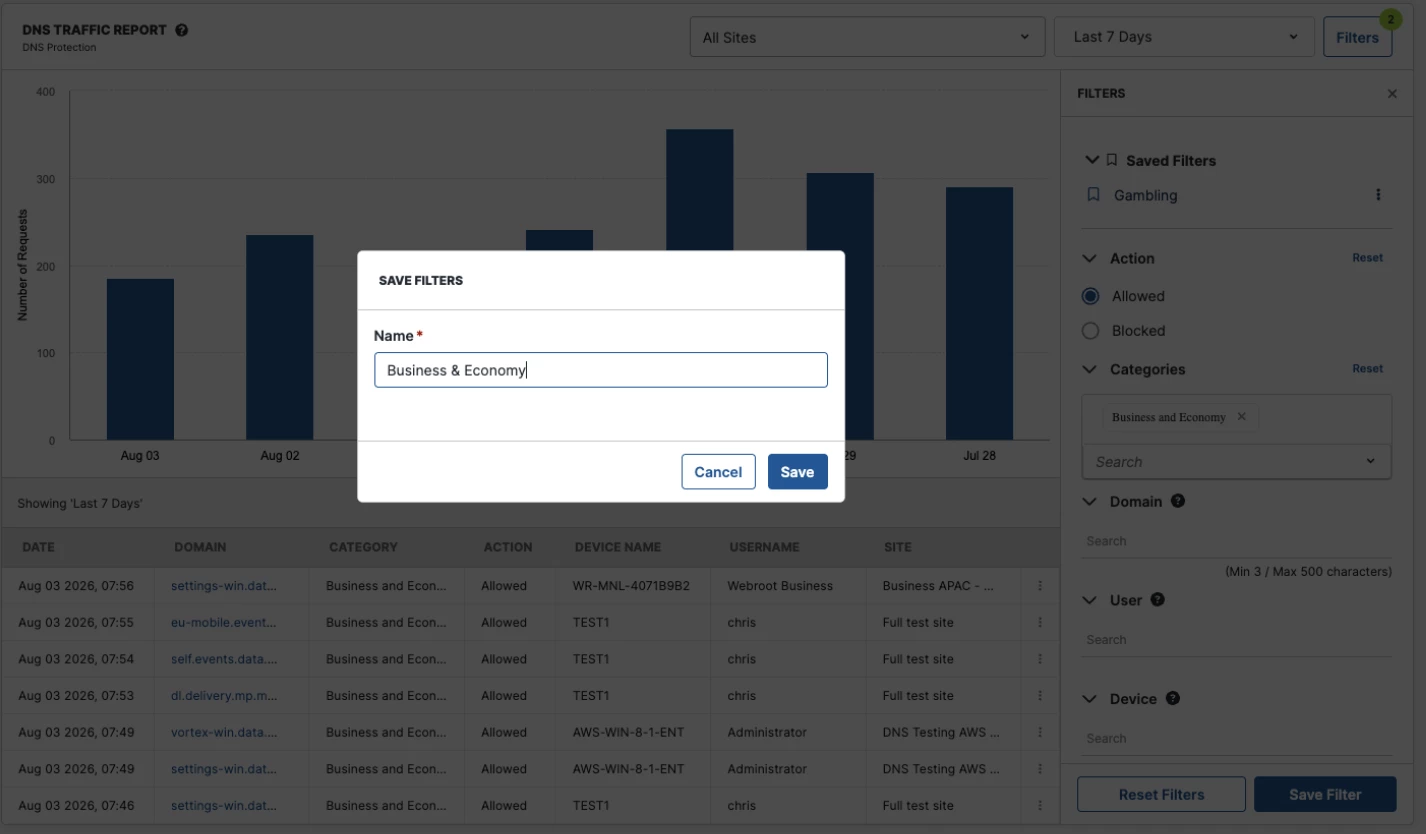
Save a filter for easy one-click results
This gives partners more precise, faster access to DNS activity, making it easier to investigate specific domains, users, or devices, and to repeat common searches without rebuilding filters each time.
Several other reports also gain filtering capabilities.
As of today these are all available under Reports > DNS
Webroot Mobile Security iOS App- V 8.4
What is being released?
We are very pleased to announce the release of the Webroot Mobile Security V 8.4 iOS App in the Appstore. The updated app is available in the Appstore: https://apps.apple.com/us/app/webroot-mobile-security/id460986853?platform=iphone.
New Features:
Text SMS Scam Protection
SMS-based phishing (commonly known as Smishing) and SMS spoofing are among the most prevalent mobile attack vectors, accounting for over 30% of mobile threats - a figure that continues to rise. We are introducing Webroot Text SMS Scam Protection for iOS, a security feature designed to detect and filter malicious text messages and protect the Webroot Secure Anywhere Plus and above license users.
-
ML-Based Detection: Automatically scans incoming SMS messages for malicious URLs using BrightCloud threat intelligence system.
-
Filtering: When a potentially harmful SMS containing a malicious link is detected, the message is automatically moved to the Spam folder, helping keep users protected from phishing and scam attempts.
Seat Count Restriction
-
License Activation: All consumer license keycodes are now get activated directly within the app. Activated devices will be accurately displayed in the My Account Portal, providing improved visibility and device tracking.
-
New Log Out functionality: Users can now securely log out of the application and sign in with a different account when needed. Navigate to Profile > Log Out. Upon logout, the device is automatically removed from the My Account Portal, and the License seat usage is updated accordingly, ensuring accurate device counts across accounts.
General Improvements
-
Allow to Renew: Previously, users with an expired keycode were prevented from accessing the application and could only add a new keycode. With this release, users can continue to access the app, and expired licenses can be renewed directly after signing in.
-
Security updates, high priority bug fixes and performance optimizations
Webroot Web Threat Shield Support for Claude.ai and other improvements
Sales Position & Related Features:
Our latest annotation and PII features are now available on claude.ai. With the release of Claude support, Web Threat Shield completes its initial strategy for extending both Chatbot Annotation (CBA) and PII Protection across the major AI chat experiences used by consumers today, including Google Gemini, Google AI Mode, ChatGPT, and Claude.
This milestone represents a significant evolution of Web Threat Shield. Historically, browser security products have focused on websites, URLs, and downloads. As users increasingly rely on AI assistants to search, research, create content, and make decisions, WTS is expanding protection to where users are spending more of their time: the AI conversation itself. CBA helps users evaluate the trust and safety of AI-generated content through in-line annotations, while PII Protection helps prevent accidental disclosure of sensitive information before it is submitted to supported AI chat experiences.
Together, these capabilities establish the foundation for a new generation of AI-aware protections within Web Threat Shield. By bringing security, trust, and privacy signals directly into the AI workflows users engage with every day, WTS continues its evolution from a traditional web protection product into a broader platform for safer digital interactions. This release completes the first phase of that vision and creates a strong foundation for future innovation in AI trust, privacy awareness, and contextual risk protection.
Position this feature as:
-
A key step in the evolution of Web Threat Shield from traditional web threat protection toward modern, AI‑aware browsing safety. As adoption of AI assistants continues to accelerate, WTS is uniquely positioned to deliver contextual trust, privacy, and risk signals directly within the user's workflow, helping ensure that security evolves alongside the way people use the web.
-
WTS extends protection beyond links and destinations to the content itself, a crucial cybersecurity proposition as users increasingly rely on AI assistants for search, research, and decision‑making,
-
CBA establishes the foundation for a broader set of innovation features focused on AI trust, response quality awareness, and contextual risk signaling, positioning WTS as one of the first consumer security solutions to actively adapt to how users interact with AI on the web today.
Additional improvements and fixes are included as part of this release, see details below.
What is being released?
-
WTS extension v2.3.26191.1
-
PII Claude support
-
CBA Claude support
-
Extend PII feature to Google inline AI mode
-
Port Collision handling logic
OpenText Server Backup Portal 9.60
What is being released?
OpenText Server Backup Portal 9.60
New Features and Enhancements
-
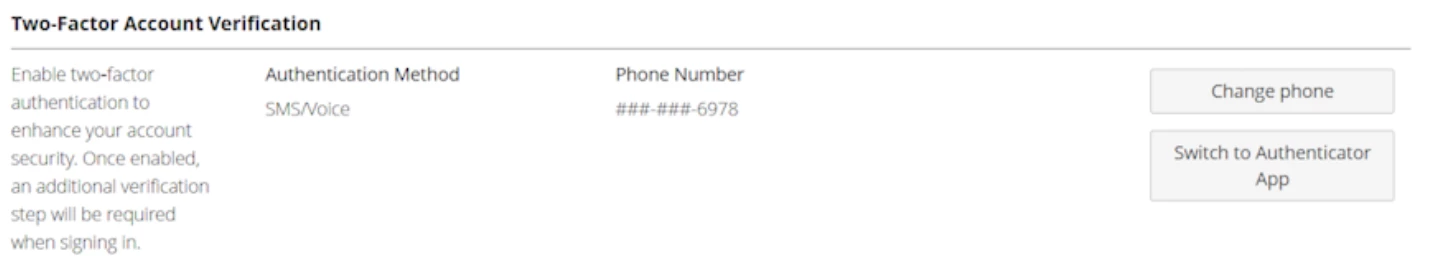
Multifactor Authentication (MFA) with Authenticator Apps
-
Added support for Microsoft Authenticator, Google Authenticator, and other TOTP-authenticator applications as an alternative to SMS and voice-based MFA.
-
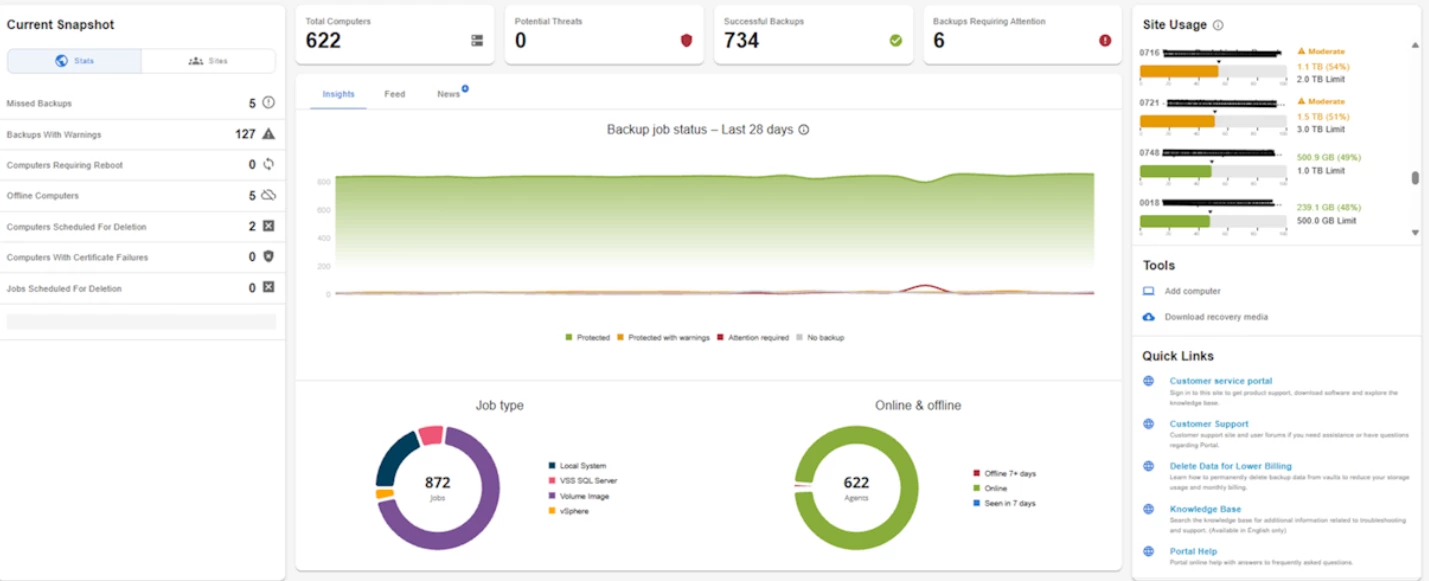
Modernized Dashboard Experience
-
Redesigned dashboard with enhanced visibility into backup health, ransomware alerts, agent status, and backup activity trends.
-
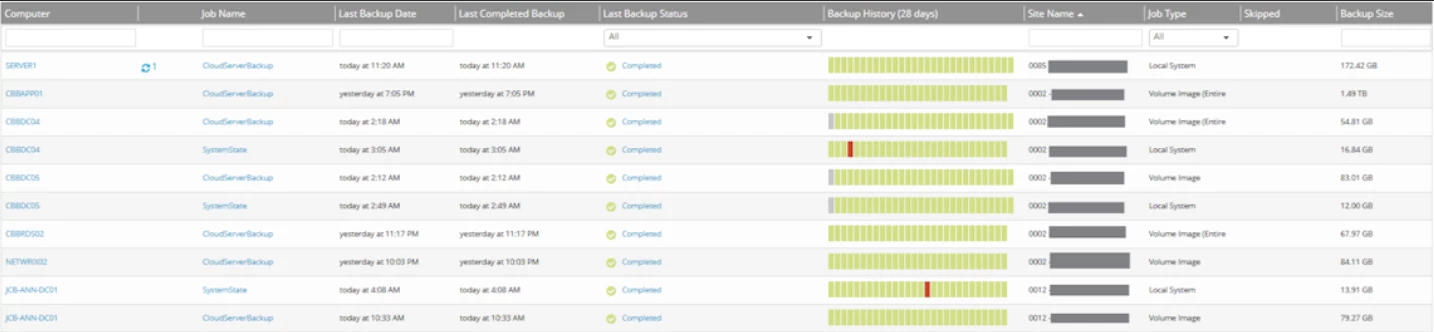
Enhanced Backup Monitoring & Reporting
-
Added 28-day backup history visualizations on both the Dashboard and Monitor pages, providing improved visibility into backup success rates and historical trends.
-
Platform Improvements
-
Updated localization for recently introduced features.
-
Improved user experience through workflow and usability enhancements, including clearer Hyper-V backup retry information.
-
Security Improvements
-
Added security enhancements to strengthen the overall Portal security posture.
Defect Fixes
-
Resolved issues affecting agent and job viewing in rare scenarios.
-
Fixed site deletion errors that could result in internal server errors.
-
Eliminated agent registration logging errors.
-
Resolved issues related to registration-only usernames containing special characters.